Your dealership may already have cybersecurity software, multi-factor authentication (MFA), backups, employee training, and a cyber insurance policy. Those are all important pieces of the puzzle, and having them in place is certainly better than not having them.
The problem is that having the right tools can sometimes create more confidence than clarity. A Controller may assume the backups are covered because the reports are green. A General Manager may hear that MFA is enabled and assume account security is handled. Employees completed phishing training, so leadership assumes someone will recognize the next convincing fake email. Maybe all of that is true, but I would still rather verify it than build a cybersecurity plan around the assumption.
Good dealership cybersecurity is not about buying one product or checking one box. It is about knowing which systems and accounts are protected, where the gaps may be, who owns each responsibility, and what happens when one layer of protection does not work.
That distinction matters at a dealership because the technology environment is rarely simple. Sales, service, finance and insurance (F&I), accounting, the business development center (BDC), and management may depend on different combinations of email, dealer management systems (DMS), customer relationship management (CRM) platforms, lender systems, OEM portals, banking applications, phones, Wi-Fi, and outside vendors. Leadership does not need to understand the technical details behind every one of them, but someone should be able to give leadership a clear answer about how the important pieces are being protected.
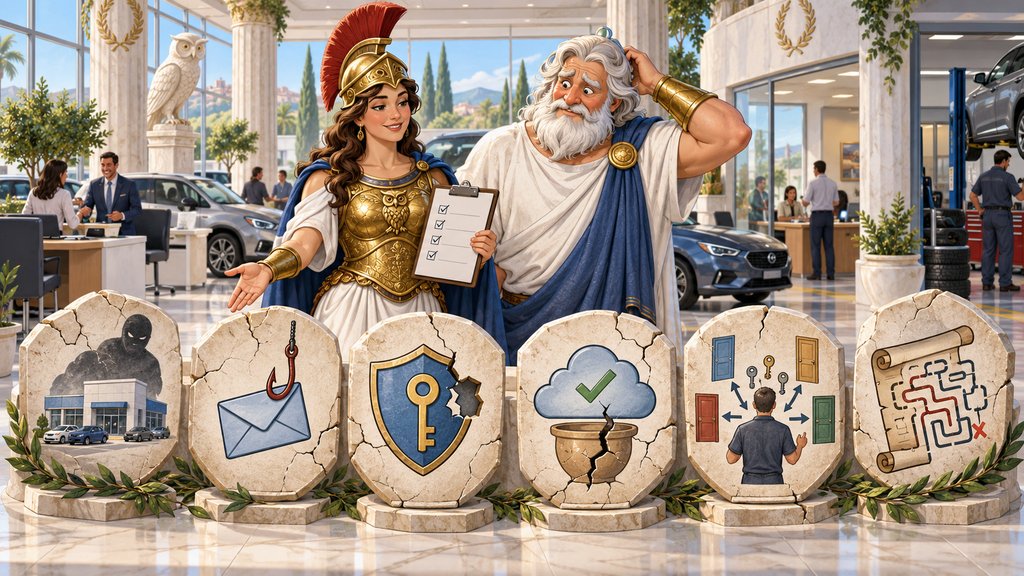
Here are six cybersecurity assumptions I would want dealership leadership to recheck.
Myth 1: "We Are Not Big Enough for Cybercriminals to Care About"
Most cyberattacks are not aimed at one specific dealership. They look for exposed systems, stolen passwords, vulnerable accounts, or employees who can be tricked, so being smaller does not make a dealership invisible.
A single-rooftop dealership may seem small compared with a national dealer group, a bank, or a Fortune 500 company. The problem with that reasoning is that an attacker does not necessarily have to know or care who you are before trying to get in.
A lot of cybercrime is opportunistic. Attackers look for exposed systems, stolen passwords, vulnerable accounts, unpatched software, and people they can trick. A dealership can become part of that process simply because an employee password was stolen, somebody responded to a convincing email, or an internet-facing system had a weakness.
Dealerships also have a complicated mix of information and access worth protecting. A Controller may have access to banking and accounting systems. F&I employees work with lender platforms and financial information. Sales and BDC employees live in email and the CRM, while managers and department leaders may have access to systems that an entry-level employee does not.
Add Microsoft 365, payroll, HR systems, OEM portals, vendor accounts, remote access, and the DMS, and the better question is not whether the dealership is important enough for an attacker to notice. The useful question is: if somebody gets access to one employee or one system, what can they reach from there? That is something leadership and IT can actually review.
Myth 2: "Our Employees Will Recognize a Phishing Email"
Some phishing attempts are obvious, but the more convincing ones look like ordinary dealership business. Training helps, but it cannot guarantee that every employee will catch every fake invoice, login prompt, account alert, or request from management.
Some phishing emails are still easy to spot. The spelling is terrible, the request makes no sense, or the sender's address looks like somebody fell asleep on the keyboard. The better ones are much harder.
At a dealership, a convincing message does not have to look unusual. It might appear to be an updated invoice from a vendor, a document that needs to be reviewed before a deal closes, a Microsoft 365 sign-in request, an OEM notification, a payroll message, a request from management, or an account alert from a system the employee actually uses.
Now put that message in front of someone who is already busy. Sales is following up with customers, the BDC is working leads, F&I is trying to finish a deal, service advisors have customers waiting, and accounting is trying to get through month-end. An urgent request can fit pretty naturally into that kind of workday.
Training helps, and good email security helps, but neither means every employee will recognize every attempt. What I would want to know is what happens when an employee is unsure. If accounting receives new payment instructions from a vendor, how are they verified? If an employee gets an unexpected Microsoft 365 login request, who do they ask? If a manager appears to request sensitive information by email, is there a simple way to confirm the request another way?
You do not need every employee to become a cybersecurity expert. You need employees to recognize when something deserves a second look and make it easy for them to ask before they act.
Myth 3: "MFA Means Our Accounts Are Protected"
MFA is one of the best controls a dealership can use, but saying that the dealership has MFA does not explain which systems it covers. The gaps are often found in accounts that were never brought under the same standard.
Multi-factor authentication is one of the most useful security controls a dealership can put in place. I recommend it, and I would much rather see an important account protected by MFA than by a password alone. Still, saying that the dealership has MFA is not really enough information.
A dealership may use Microsoft 365 for email, separate credentials for its DMS and CRM, different sign-ins for OEM and lender portals, banking applications, vendor systems, remote access, and administrative accounts. Those systems are not necessarily managed by the same company or protected in exactly the same way.
So when someone tells me a dealership has MFA, the next thing I want to understand is where it is actually enabled. Is it protecting email, remote access, administrator accounts, banking and financial systems, and other important cloud applications? Are there older employee or vendor accounts that were never brought under the same standard?
The type of MFA matters too. Attackers can sometimes trick users into approving a login or entering a verification code into a fake sign-in page, and stolen authenticated sessions can create another path around the password-and-code process. That does not make MFA ineffective. It means MFA should be one layer of the security plan rather than the point where the conversation ends.
Myth 4: "Our Backups Have Us Covered"
A green backup report tells you that a job ran. It does not tell you what the dealership can actually recover, whether recovery has been tested, or who is responsible for each system.
A successful backup report tells you that a backup job completed. That is useful information, but it does not necessarily tell the Controller or General Manager what the dealership can actually recover when something goes wrong.
Dealership technology also creates an ownership question. Some information may be backed up directly by the dealership or its IT provider, while other systems may be hosted and managed by outside vendors. Simply saying "the DMS is in the cloud" or "the vendor handles that" does not explain what the dealership is responsible for, what the vendor protects, or how information would be recovered after a serious problem.
That is why I separate backup from recovery. A dealership should understand what is being backed up, what is not, when recovery was last tested, who starts the recovery process, and what needs to come back first.
If email or an important internal system became unavailable tomorrow, what would sales, service, F&I, and accounting need first? Who would contact the outside vendors? If one system came back before another, what could employees actually do? Those are business-continuity questions, not just backup questions.
You can have perfectly good backup software and still have an incomplete recovery plan. The backup is the technical tool. Getting the dealership working again is the business outcome.
Myth 5: "Cybersecurity Is IT's Responsibility"
IT can only manage what it knows about. Access changes, vendor relationships, and business decisions happen across departments, so cybersecurity ownership has to reach beyond the IT department too.
IT has a major role in cybersecurity, but it cannot manage access it does not know about, and it cannot make business decisions on its own.
Say an employee leaves the dealership. IT may remove Microsoft 365 access and disable the employee's computer account, but what about the CRM, DMS, OEM systems, lender portals, payroll application, vendor websites, and any shared accounts the employee knew about? If different departments own different systems, someone needs a process that makes sure the entire list gets reviewed.
The same issue comes up when a department adds a new cloud application, a vendor needs remote access, accounting receives a request to change payment instructions, or leadership approves a company that will handle customer information. Technology may be involved, but those are not decisions IT can make in isolation.
There is a regulatory reason this cannot sit with IT alone, either. For dealerships covered by the FTC's Safeguards Rule, the information security program is broader than simply installing security software. The exact obligations depend on the dealership's situation, so legal or compliance questions should be reviewed with qualified counsel. From an IT standpoint, though, the point is simple: management, department leaders, employees, vendors, and IT may each own a piece of cybersecurity.
Someone still needs visibility across the whole thing.
Myth 6: "We Know What to Do If Something Happens"
Having a general idea of what to do is not the same as having a practical, tested process. Many gaps in incident response become visible only when someone tries to follow the plan.
Most people have a general idea of what they would do after a cybersecurity incident: call IT, tell the manager, and maybe disconnect the computer. That is a reasonable start, but an actual incident gets complicated quickly.
An employee notices something suspicious on a workstation. Should the computer be disconnected from the network? Should it be turned off? Who calls IT? Who informs the General Manager, Dealer Principal, or Controller? Does the cyber insurance carrier need to be contacted before certain work is performed?
Then there are the dealership-specific vendors. If the problem affects email, the DMS, CRM, phones, lender access, or another outside system, who coordinates those companies? If email itself is unavailable, how does leadership communicate instructions to employees? Those are much easier questions to answer before everyone is under pressure.
A dealership does not need a hundred-page incident-response manual that sits in a binder and never gets opened. It needs a practical process people can follow, current contact information, clearly assigned responsibilities, and a way to communicate if normal systems are unavailable.
Then test it once in a while. A tabletop exercise will usually uncover a question nobody thought about, which is precisely why it is useful to discover the question before an actual incident.
The Bigger Myth: Buying Security Means You Have Security
There is a common thread running through all six of these myths. A dealership can buy very good technology, work with reputable vendors, train employees, require MFA, maintain backups, and carry cyber insurance, yet leadership can still be left with unanswered questions.
That does not mean the dealership made bad decisions. Technology environments change. Employees join and leave, people move between departments, new applications are added, vendors change, remote access gets created, dealership groups add rooftops, and security requirements evolve. Over time, the bigger risk is assuming the environment still works exactly the way everyone thinks it does.
The way I look at it, dealership leadership should not have to become technical enough to personally verify every cybersecurity control. But the Controller, General Manager, or Dealer Principal should be able to ask reasonable questions and get clear answers.
Who has access? Where is MFA enabled? What information is protected? What is being monitored? What has actually been tested? Which vendors have access to the environment? Who owns the response when several companies are involved?
If the answer to one of those questions is "I think so," that does not automatically mean there is a problem. It does mean there is something worth verifying.
A Practical Way to Get From Assumptions to Clear Answers
I would keep the process simple and focus on three things: what is in place, which assumptions matter most, and who owns the outcome.
1. Review What Is Actually in Place
Start with the systems, accounts, cybersecurity controls, backups, vendors, remote access, and employee processes the dealership depends on today. The goal is not to find fault with somebody's previous decision. It is to get an accurate picture of the environment as it exists now.
2. Verify the Important Assumptions
Do not stop at "we have backups," "we use MFA," or "the vendor handles security." Confirm what is covered, where the exceptions are, when important controls were last tested, and who is responsible for anything that sits outside IT's control.
3. Decide Who Owns the Outcome
Dealerships will always have multiple technology vendors. The DMS company should handle its platform, the internet provider should handle its connection, and other vendors should handle the systems they provide. But the dealership should not have to referee them.
When an issue crosses those boundaries, someone needs to understand how the pieces fit together, coordinate the right companies, keep leadership informed, and stay with the problem until there is a clear answer.
Six Questions I Would Ask Your IT Provider
If dealership leadership wants a quick place to start, ask:
- Where is MFA enabled today, and which important systems or accounts are not covered?
- How are employees trained to recognize suspicious requests, and what should they do when they are unsure?
- What dealership information is backed up, what is handled by outside vendors, and when was recovery last tested?
- How are employee and vendor accounts reviewed when someone leaves, changes roles, or no longer needs access?
- Who coordinates cybersecurity responsibilities that involve leadership, employees, IT, and outside vendors?
- What exactly happens during the first hour after someone suspects a cybersecurity incident?
The answers should not require a degree in computer science to understand. A Controller or General Manager should be able to hear the explanation and understand what is protected, what still needs attention, and who is responsible for the next step.
That is the difference between hoping cybersecurity is handled and knowing where the dealership actually stands.
Frequently Asked Questions
Does Having Cyber Insurance Mean Our Dealership Is Protected?
Cyber insurance can help with certain costs after an incident, but it does not replace the underlying security work. If the dealership's application or renewal questionnaire asks about controls such as MFA, backups, or access management, those answers need to reflect what is actually in place.
What Does the FTC Safeguards Rule Require of Auto Dealerships?
For dealerships covered by the Rule, the FTC requires a written information security program designed to protect customer information. The FTC's automobile dealer guidance says the Rule applies to most automobile dealers that finance or lease automobiles. Because the exact obligations depend on the dealership's activities and circumstances, legal or compliance questions should be reviewed with qualified counsel.
How Often Should a Dealership Test Its Backups?
There is no single schedule that fits every dealership. The right frequency depends on the systems involved, how often information changes, the dealership's recovery needs, and any contractual, insurance, or regulatory requirements. What matters is that recovery testing is planned, documented, and repeated rather than treated as a one-time setup task.
Get a Clearer Picture of Your Dealership's Cybersecurity
Cybersecurity should not become one more thing dealership leadership has to chase. Tech Marvel combines dealership IT experience with over 30 years of technology expertise to help New Jersey dealerships reduce downtime, strengthen cybersecurity, coordinate technology vendors, and get clear answers from one accountable local partner.
For dealerships in Morris County and Northern New Jersey, we can help review the systems, accounts, vendors, backups, security controls, and response processes your team depends on every day. The goal is not to sell you another security product. It is to help you understand what is working, what should be verified, and who owns the next step.
Schedule Your Free 20-Minute Dealership IT Review
We will talk through your current environment, recurring concerns, cybersecurity priorities, vendors, and any questions leadership has not been able to get answered clearly.
Not ready for a review? Get the Plain-English Guide to the IT Questions Every Dealership Should Ask Before Switching Providers and use it to start the conversation with your current IT company.