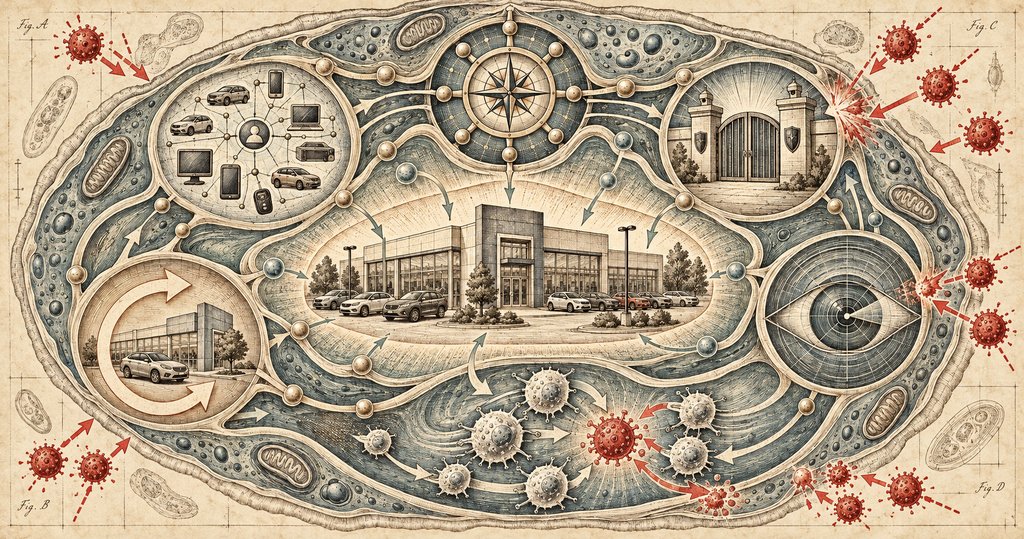
A Controller asks a reasonable question before a cyber insurance renewal or leadership meeting: What are we doing to protect the dealership? The answer may include email filtering, multi-factor authentication, endpoint security, a firewall, backups, employee training, security monitoring, and protections supplied by several outside vendors.
That sounds reassuring, and every one of those protections may be useful. The harder question is whether anyone can explain what each layer protects, where the gaps are, who reviews the alerts, and what happens when one layer does not stop the problem.
A medicine cabinet can be full without proving that the person who owns it is healthy. Dealership cybersecurity works the same way. A long list of products may show that money has been spent, but the list alone does not tell leadership whether the dealership has a coordinated way to prevent problems, recognize suspicious activity, respond, and recover.
An auto dealership does not need the largest possible collection of cybersecurity tools. It needs a coordinated security system in which each layer has a clear purpose, important alerts reach someone who will act, recovery is tested, and leadership knows who owns the outcome when several vendors are involved.
The immune-system comparison is useful because an immune system does more than block every possible threat at the door. It recognizes trouble, communicates, responds, learns, and helps the body recover. Your dealership's cybersecurity should work with the same kind of coordination, even though the individual protections may come from different companies.
Why More Security Products Do Not Automatically Mean Better Security
Additional security layers can improve protection, but only when each one addresses a real risk, is configured for the environment, and fits into a response process someone actually manages.
Dealership cybersecurity rarely starts with a blank sheet of paper. A new insurance question leads to one product. A phishing concern adds another. The Microsoft 365 provider enables a security feature, the firewall company offers a service, and the backup vendor solves a different problem. Each decision can make sense when it is made.
Over time, however, the dealership may end up with overlapping tools in one area and little protection in another. Two products may both generate alerts, but nobody knows which alert matters or who receives it. A system may be protected against malware while an old vendor account, weak approval process, or untested recovery plan creates a completely different path to disruption.
The issue is not that the dealership bought the wrong products. Technology, staffing, vendors, and insurance expectations change. The issue is whether anyone periodically steps back and uses an auto dealership IT risk assessment to look at the collection as one operating system instead of a series of unrelated purchases.
What a Healthy Dealership Cybersecurity System Should Do
The National Institute of Standards and Technology's Cybersecurity Framework 2.0 organizes cybersecurity outcomes around six functions: govern, identify, protect, detect, respond, and recover. A dealership does not need to turn that framework into a complicated internal project, but those functions provide a useful leadership test.
If most of the conversation is about products that protect devices, leadership may still be missing the rest of the system. Who governs the program? What systems and accounts have been identified? How is suspicious activity detected? Who responds? How does the dealership recover? Those questions are much closer to the real business outcome than asking how many security products are installed.
The Layers Have Clear Jobs
Every important layer should have a reason to exist. Email security may reduce malicious messages. MFA may help protect accounts when a password is stolen. Endpoint security may detect suspicious behavior on a workstation. Backups support recovery when information is damaged, deleted, or encrypted.
Leadership does not need the technical configuration for every tool. It should be possible, however, to explain what the tool protects, which users or systems it covers, what it does not cover, and which person or company is responsible for managing it.
The Layers Work Together
No single layer should be expected to stop every problem. A convincing phishing email may get through the filter, but an employee may question it. If the employee enters a password into a fake page, MFA may add another obstacle. If an attacker still gets access, monitoring may identify unusual activity and start a response.
That is layered security. The value comes from the handoffs between layers, not simply from the number of products. When those handoffs are unclear, each product can appear healthy on its own while the dealership still lacks a coordinated response.
Important Alerts Reach a Person
Security tools can generate a great deal of information. Some alerts are routine, some need investigation, and a small number may require quick action. The dealership should know which company or person receives the important alerts, whether they are reviewed, and what happens after something suspicious is found.
A green dashboard only tells part of the story. If nobody is responsible for interpreting the warning and coordinating the next step, the dealership has monitoring without much response. That is the cybersecurity equivalent of a smoke detector sounding in an empty building.
The Dealership Can Recover
Protection and detection receive a lot of attention because they feel immediate. Recovery is easier to assume, especially when dealership backup reports are arriving and appear successful.
The useful question is what the dealership can actually restore and whether the process has been tested. Email, internal files, Microsoft 365 data, servers, workstations, and information held inside vendor platforms may all have different backup responsibilities. A dealership should understand those boundaries before an incident forces everyone to figure them out under pressure.
Someone Owns the Whole Picture
A dealership will always have multiple technology vendors. The DMS provider owns its platform. The internet company owns the connection. Other companies may manage phones, CRM, payroll, cameras, backups, email security, or specific applications.
When dealership technology vendors blame each other, the Controller or General Manager should not have to become the referee. One accountable IT partner should be able to explain how the major layers fit together, identify where another vendor must be involved, coordinate the response, and stay with the issue until leadership has a clear answer.
Where Dealership Security Collections Commonly Lose Coordination
The most important gaps often appear between products, systems, departments, and vendors rather than inside the security tool leadership is looking at.
Consider Microsoft 365 and the dealership's other cloud accounts. Email may have strong MFA and monitoring while the DMS, CRM, OEM portals, lender systems, payroll platform, banking applications, and vendor websites follow different rules. Saying that the dealership has MFA does not answer which important accounts are covered.
The same problem can appear with employee changes. IT may disable the computer and email account after a departure, while department-managed or vendor-managed accounts remain active because nobody included them in the request. Every individual company completed its part, but the dealership still has an access gap.
Alerts create another boundary. The firewall vendor may see one signal, the endpoint provider may see another, and Microsoft 365 may record suspicious activity in a separate place. If no one is expected to connect those observations, the dealership can have several useful tools without anyone seeing the complete event.
Backups also cross vendor boundaries. The dealership may control some backups while the DMS, CRM, payroll, or other cloud vendors control their own environments. Leadership should know what the dealership can restore, what depends on the vendor, and who starts each recovery process.
When Overlap Is Useful and When It Becomes Waste
Overlap is not automatically a problem. It becomes a problem when the dealership cannot explain why the overlap exists, who manages it, or whether the added complexity improves the outcome.
Some overlap is intentional. Email security and endpoint protection may both inspect different parts of the same attack. MFA and login monitoring may address related account risks in different ways. Backups may use more than one location or method because the dealership has different recovery needs.
The tradeoff is complexity. Multiple tools can create duplicate alerts, competing settings, additional licensing costs, and uncertainty about which company is responsible. Removing overlap without understanding it can weaken protection, but continuing to pay for every product forever does not make sense either.
I would not begin by cancelling tools or adding another one. I would begin by asking what risk each product addresses, what systems it covers, who manages it, and what would be missing if it were removed. That gives leadership a business reason for the decision instead of turning the review into a contest over the longest feature list.
Questions Dealership Leadership Should Ask
A Controller, General Manager, or Dealer Principal does not need to understand every technical setting. Leadership should be able to ask these questions and receive answers in normal business language:
- What are our major cybersecurity protections, and what specific risk does each one address?
- Which employees, devices, locations, systems, and cloud accounts are covered by each protection?
- Where do we intentionally have overlapping protection, and why?
- Which important systems or accounts sit outside our standard security controls?
- Who receives and reviews security alerts from each tool?
- What happens after an alert suggests that an account or device may be compromised?
- Which outside vendors have access to dealership systems or information?
- What can we restore ourselves, what depends on an outside vendor, and what recovery has actually been tested?
- Who coordinates the response when several security tools, departments, or vendors are involved?
An answer such as 'the vendor handles it' may be correct for one piece of the environment. Leadership should still know which vendor, what that company handles, where its responsibility ends, and who is responsible for the next step.
A Practical Three Step Cybersecurity Checkup
This does not need to begin as a large consulting project. The first pass should give leadership a clear map of what exists, why it exists, and what happens when something goes wrong.
1 Inventory the Protections and Responsibilities
List the major security products and services, the systems they cover, the company that manages each one, the alerts they produce, and the business owner inside the dealership. Include vendor-hosted platforms and department-managed accounts, not only equipment controlled by IT.
2 Map the Handoffs
Walk through a few realistic situations. An employee reports an unexpected MFA prompt. Accounting receives new banking instructions. A salesperson clicks a questionable link. A former manager still appears in an OEM portal. A backup needs to be restored. For each situation, identify who acts first, who must be informed, and which vendor owns the next step.
3 Confirm Response and Recovery
Choose a small number of important scenarios and verify that the process works. Confirm that alerts reach the right people, contact information is current, employees know how to report a concern, and recovery responsibilities are understood. A tabletop conversation or limited recovery test can reveal assumptions before they become part of an actual incident.
The Goal Is a System Leadership Can Explain
Good dealership cybersecurity does not need to look impressive on a slide. It needs to support the business on an ordinary Tuesday and give people a workable plan on a very bad Friday.
That means the dealership can explain what is protected, where important exceptions exist, who watches for trouble, who responds, and how the business recovers. It also means leadership can get one clear answer when the issue crosses Microsoft 365, employee devices, the network, backups, the DMS, another vendor platform, or the cyber insurance process.
If the dealership already has the right protections, a coordinated review may confirm that the system is working as intended. If it reveals duplicate costs, uncovered accounts, unmonitored alerts, or unclear responsibilities, leadership can prioritize those issues instead of automatically buying the next product someone recommends.
The goal is not more security software. The goal is a dealership that knows how its protections work together and who owns the outcome when something needs attention.
Frequently Asked Questions
How many cybersecurity tools should an auto dealership have
There is no useful magic number. The right combination depends on the dealership's systems, users, locations, vendors, risks, insurance questions, and existing controls. Each tool should have a clear purpose, defined coverage, an owner, and a place in the response or recovery process.
Is overlapping cybersecurity protection a waste of money
Not necessarily. Some overlap provides intentional layers of protection. It becomes questionable when nobody can explain why two tools are doing similar work, whether both are managed, or what additional protection the dealership receives for the added cost and complexity.
Does the DMS provider handle dealership cybersecurity
The DMS provider is responsible for the platform and services it supplies. The dealership still depends on computers, networks, email, Microsoft 365, user accounts, remote access, backups, other cloud applications, and internal processes that may sit outside the DMS provider's responsibility. Someone should coordinate the boundaries when an issue involves more than one system.
Who should monitor dealership cybersecurity alerts
The answer depends on the dealership's agreements and security services, but the responsibility should be explicit. Leadership should know which provider or internal person receives important alerts, when they are reviewed, how incidents are escalated, and who coordinates the business response.
Get a Clearer Picture of How Your Security Fits Together
Cybersecurity should not become another collection of products the Controller or General Manager has to referee. Leadership should be able to get a clear explanation of what is covered, what needs attention, and who owns the response when several companies are involved.
Tech Marvel combines dealership IT experience with over 30 years of technology expertise to help New Jersey dealerships reduce downtime, strengthen cybersecurity, coordinate technology vendors, and get clear answers from one accountable local IT partner.
For dealerships in Morris County and Northern New Jersey, we can help review the major security layers, vendor responsibilities, alert paths, access controls, backups, and response processes your business depends on. The purpose is not to sell another product. It is to understand whether the protections already in place form a system leadership can rely on and explain.
Schedule Your Free 20-Minute Dealership IT Review
We will talk through your current environment, recurring concerns, cybersecurity priorities, vendors, and any questions leadership has not been able to get answered clearly.